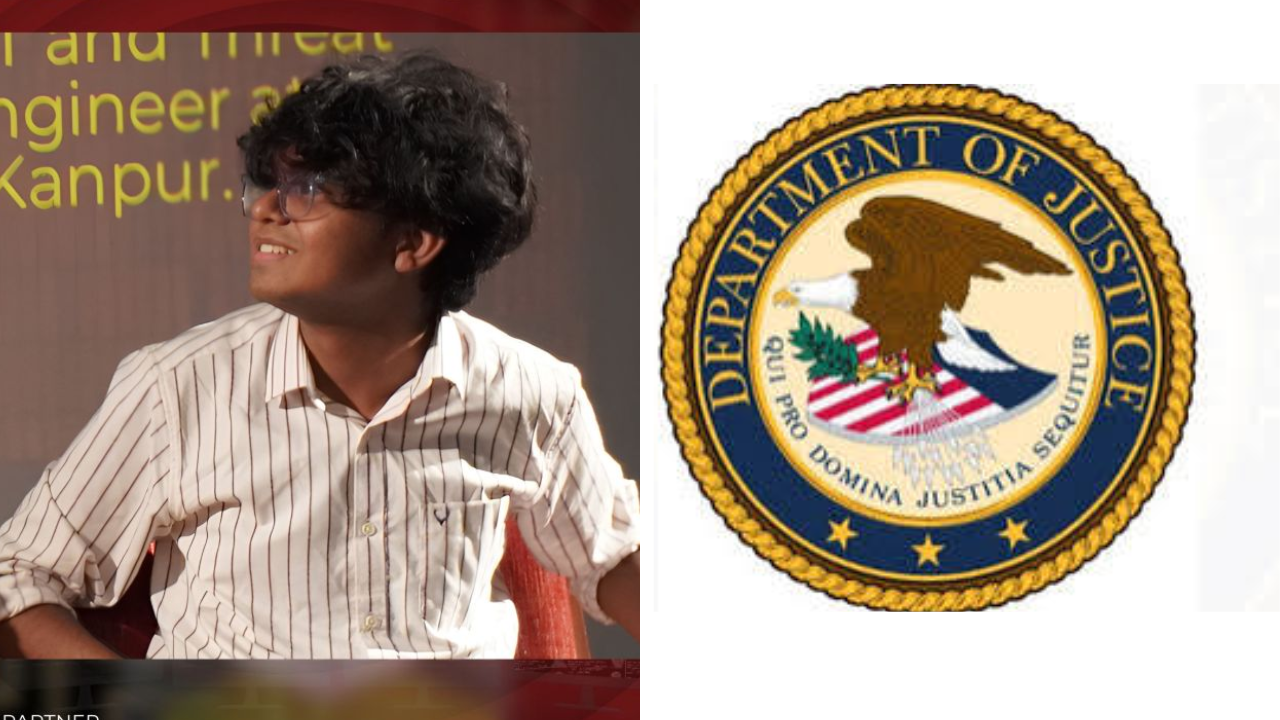
Nineteen-year-old Nisarga Adhikary did not break into the digital infrastructure of the United States Department of Justice with malicious intent or complex phishing campaigns. He simply looked where others refused to look, armed with custom scripts and an insatiable curiosity that institutional gatekeepers routinely fail to accommodate. When his name appeared on the US DOJ cybersecurity Hall of Fame after responsibly disclosing a critical flaw, it marked a profound validation for a researcher who had spent months warning authorities closer to home about fragile public portals.
Months prior to earning international recognition, Adhikary forced an uncomfortable spotlight onto India's Central Board of Secondary Education (CBSE). By identifying serious security vulnerabilities within the board's Online Submission of Marks (OSM) evaluation portal, he exposed structural vulnerabilities in systems handling millions of student records. Rather than rewarding the discovery with immediate institutional introspection, the initial response reflected a defensive posture common among legacy bureaucracies. Critical infrastructure, it turned out, was running on glass foundations. If you liked this post, you might want to check out: this related article.
The journey from exposing domestic portal gaps to securing validation from foreign law enforcement highlights a persistent structural failure in how technical talent is identified and utilized. Adhikary’s trajectory eventually led to his appointment as an Open-Source Intelligence and Threat Intelligence Engineer at C3iHub, IIT Kanpur. Yet, his early friction with the system underscores an ecosystem that often prioritizes standardized examination ranks over practical, hands-on engineering competence.
The underlying issue extends far beyond a single teenager or a patched portal. Modern digital governance relies on outsourced software vendors who frequently cut corners on security audits to meet tight bureaucratic deadlines. When educational boards and government departments deploy massive evaluation platforms, scalability and speed routinely eclipse baseline penetration testing. The result is a sprawling attack surface hidden behind official URLs, vulnerable to anyone willing to write custom scripts instead of relying on automated vulnerability scanners. For another angle on this event, see the latest coverage from TIME.
Adhikary's subsequent disclosures involving US defense and law enforcement systems emphasize the contrast in how vulnerabilities are handled globally. Organizations with mature vulnerability disclosure programs treat independent researchers as an extension of their security teams. By establishing clear, friction-free channels for responsible disclosure, federal agencies can patch critical gaps before bad actors weaponize them. When a nineteen-year-old can identify flaws in foreign military assets and domestic education portals alike, the security perimeter ceases to be geographical. It is entirely dependent on competence.
The broader educational establishment continues to measure capability through rigid testing metrics while actual engineering talent migrates toward practical exploration. Until institutional frameworks learn to collaborate with independent security researchers rather than dismissing them, digital infrastructure will remain exposed to the next script running quietly in the background.